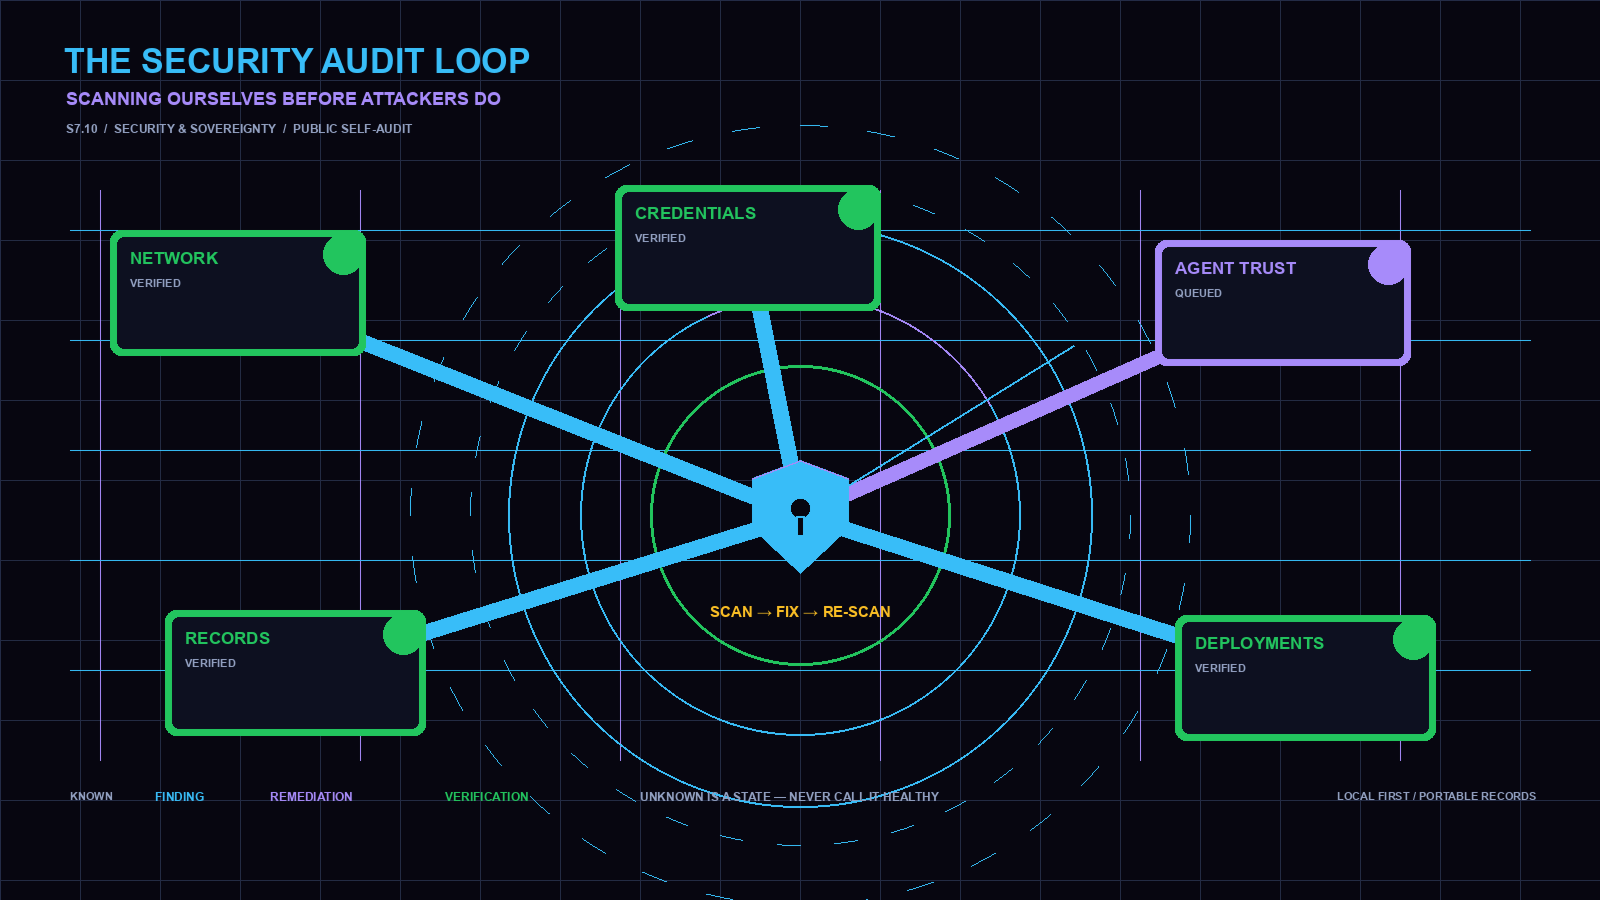

The first scan belongs to the defenders
Most security stories begin with an attacker: a breached password, an exposed service, a clever payload. A mature security practice begins earlier. It asks what the defenders can see, prove, and change before an adversary performs the same reconnaissance.
That is the security audit loop. The organization maps its own routes, inventories its credentials, checks permissions, tests boundaries, records findings, corrects them, and then scans again. The loop is not a ceremonial compliance report. It is a standing rhythm that turns the system’s own claims into current evidence.
The shift matters because infrastructure changes quietly. A container receives a broader permission, a route is left open for a deployment, a service is replaced without a matching health check, and a temporary key survives longer than the work that required it. None of these changes announces itself. Repetition reveals them.
A self-scan does not promise perfect knowledge. It shortens the interval between exposure and discovery, preserving time for a deliberate response.
Inventory before judgment
A useful audit begins with a truthful map of what exists. Name the public hosts, private endpoints, container boundaries, databases, agent profiles, signing keys, scheduled jobs, and shared state stores. Include the services that nobody considers important because they were temporary six months ago.
For every component, record a stable identifier, its role, its owner, the route through which it can be reached, the identities that may use it, and the signal that indicates health. The record should be legible to a person during an incident and machine-readable by an automated check.
Inventory turns “something is wrong” into a named route, identity, or record. Without it, each alert becomes an argument about what the system was supposed to contain.
Test boundaries from both sides
A scanner should ask bounded questions at each boundary. Which services listen where? Which routes are intentionally public? Which credentials can authenticate, and which resources can those credentials read or change? Which agents can spawn work, and which permissions follow them? Which records are writable, append-only, cached, or synchronized?
The word “bounded” is deliberate. An audit is not permission to create uncontrolled load, access unrelated data, or probe systems the organization does not operate. Scope every check to declared assets, define the expected result, and stop when evidence is sufficient. A safe audit is an experiment with a hypothesis and a boundary, not an unbounded hunt.
Useful findings have a stable shape: asset, check, observed time, expected state, observed state, severity, and next action. “The system feels secure” is not a finding. “This public route is reachable without expected authentication, observed now, and requires bounded remediation” is a reproducible record.
Findings are evidence, not verdicts
A finding should help someone decide, not trigger panic by itself. Separate observation from interpretation. Record what the check observed, then state why it matters in this system. A medium-severity open port might be irrelevant on a private network and urgent on a public edge. A missing header can be a compliance task while a compromised credential is an incident.
Severity is a routing decision. A scanner that sends every result to one queue trains people to ignore it. Group findings by consequence and confidence, identify the owner who can make the change, and attach a deadline or escalation path. Preserve the raw result so the decision can be rechecked.
The record must also say what is unknown. A failed check does not prove that a service is absent; a timeout does not prove that a port is closed. “Unknown,” “stale,” and “not run” are meaningful states. A security loop that converts missing evidence into green is manufacturing confidence.
Fix the cause, then rescan
Every finding should leave one of four trails: resolved, accepted with an owner and rationale, deferred with a dated review, or escalated as an incident. This prevents findings from becoming an unowned backlog or a risk silently closed because a scanner marked it informational.
The correction should address the class of weakness. Revoke and replace exposed credentials rather than merely hiding what they can reach. Restrict a route where it is exposed. Remove an obsolete permission rather than asking an operator to remember not to use it. Preserve evidence, then rerun the smallest check that can falsify the fix.
A successful remediation has a second half: re-audit. The original scan is a hypothesis. The rescan proves the system changed as intended. If the same finding returns under another name, the first fix was local rather than structural.
Let risk choose the cadence
Not every asset needs a full sweep every minute. A useful cadence follows consequence and change rate. A public authentication surface, a signing-key store, a database with sensitive records, and an internal documentation page should not share one schedule.
Use several layers. Run inexpensive liveness and exposure checks frequently. Run dependency and permission checks when deployments or identities change. Reserve deeper behavioral tests for critical paths and scheduled reviews. After an incident or migration, raise the cadence until the new state is understood, then return to the normal rhythm.
The loop is sustainable only when its cost matches the risk it can falsify. A full audit that exhausts the system or drowns the team is not a stronger control. The best scan is the smallest honest check that produces a decision, repeated often enough that drift cannot accumulate unseen.
Make continuity part of the security result
A scan produces a point in time. Continuity comes from connecting it to the next. Store the result, configuration context, owner, action, and verification. Keep local copies available when a remote service is unreachable; remote stores can enrich the record without becoming its only witness.
For an agent fleet, the audit record should support a bounded action. A worker should be able to distinguish “credential missing,” “route exposed,” “record stale,” and “check not run,” then stop or escalate rather than improvise. The action can be reversible, such as disabling a newly exposed optional route, or deliberately conservative, such as pausing writes until a human verifies an integrity failure.
This is where the North Star’s record principle meets security. Information is useful when it survives long enough to be compared, corrected, and learned from. A green dashboard that cannot explain its last successful check is decoration. A compact trail naming what changed and proving the next check is operational memory.
The public proof is the loop itself
Security systems do not become trustworthy because they expose every internal mechanism. They become trustworthy when they demonstrate bounded, repeatable behavior: the asset was identified, the check scoped, the result recorded, the owner acted, and the rescan verified the change.
That is the laser line for public documentation. Share the operating principle, vocabulary, escalation boundary, and evidence that the loop runs. Keep private credentials, raw customer data, hidden scoring formulas, and protected internal methods inside the vault. Proof of proficiency is valuable; a blueprint is not.
The security audit loop is a design choice: who looks first, what they can see, how the record changes the next decision, and whether the system repeats the test after deployment. Scan ourselves before attackers do, but scan as a discipline—not a panic, a performance, or a promise of invulnerability. The standard is not “we found nothing.” It is “we know what we checked, when we checked it, and what changed next.”