Go-Live Research: What Actually Worked
Go-Live Research: What Actually Worked We pushed lucidhive.com to be complete and…

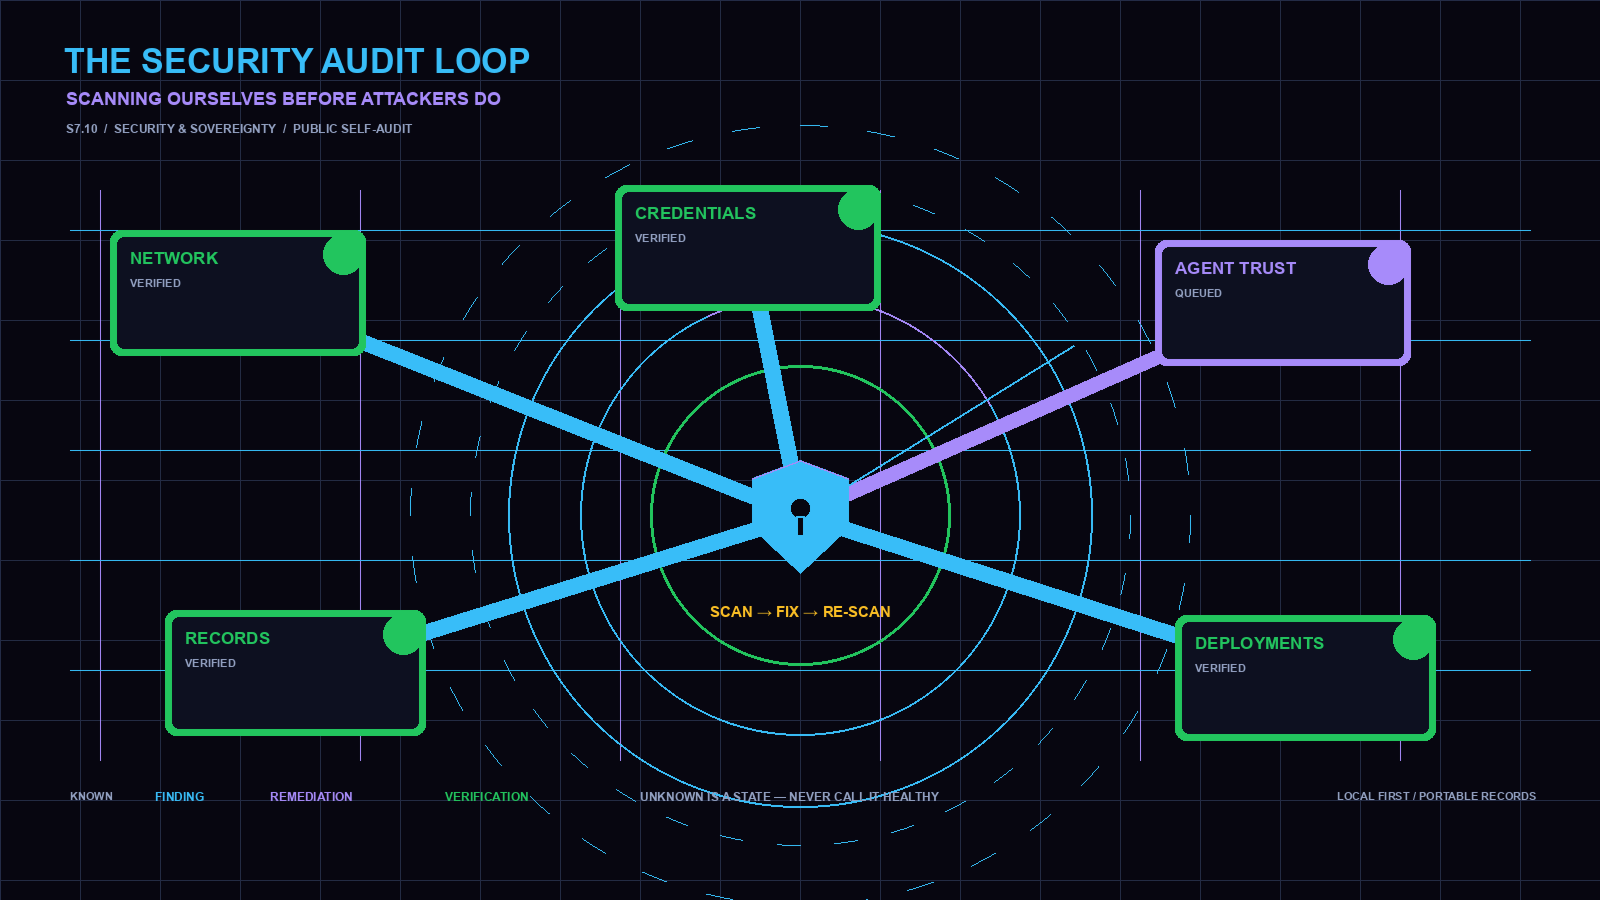
The Security Audit Loop: Scanning Ourselves Before Attackers Do
The first scan belongs to the defenders Most security stories begin with…
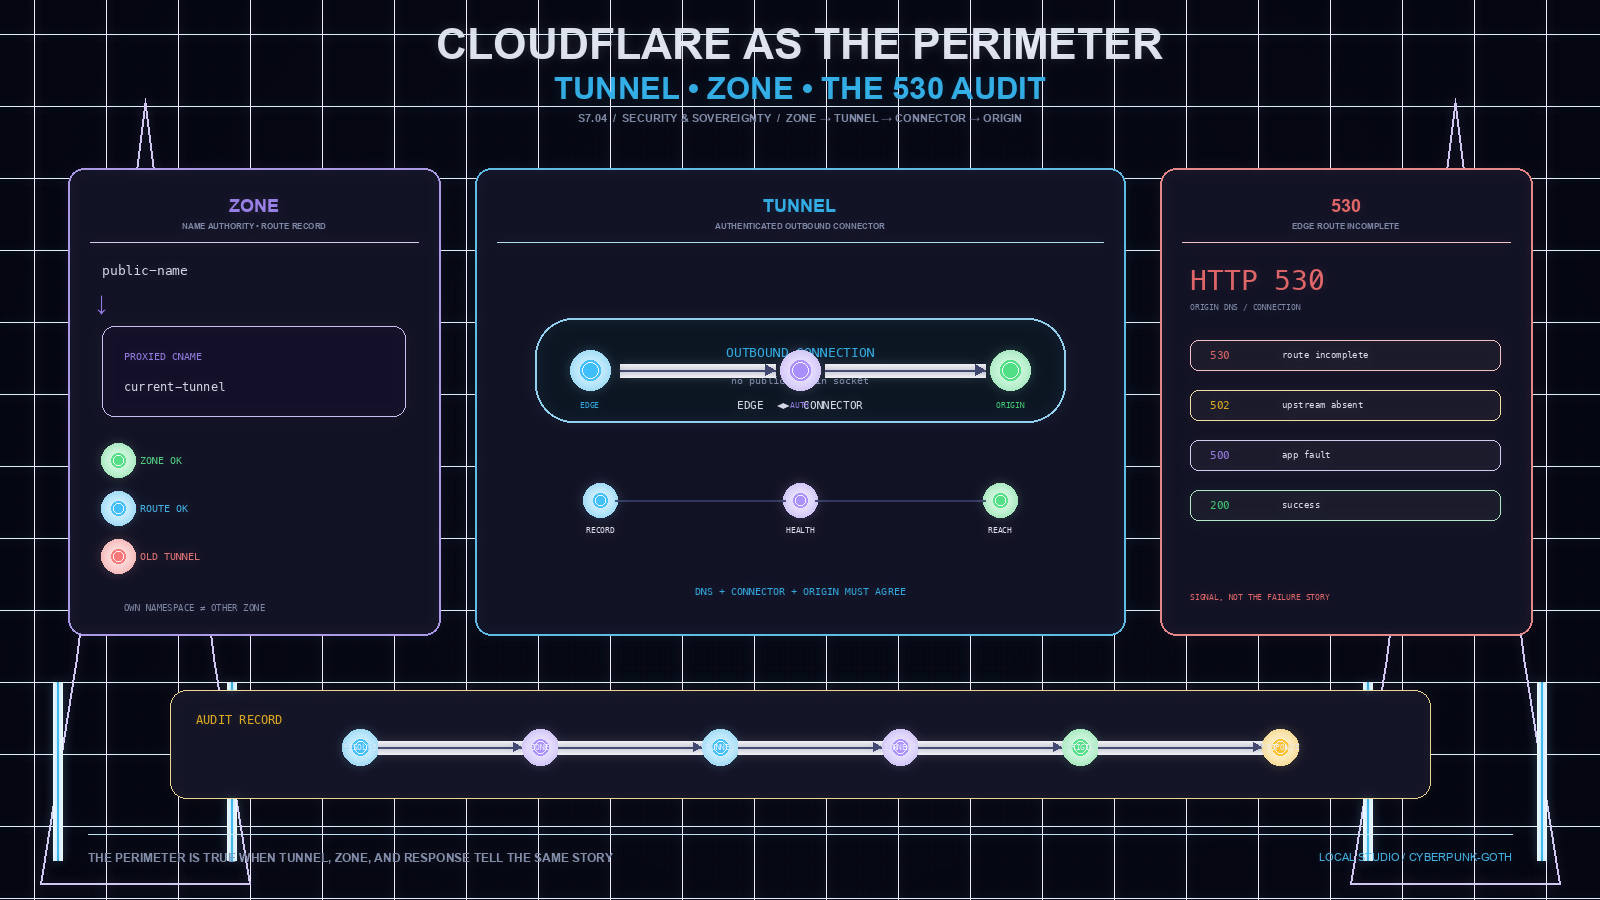
Cloudflare as the Perimeter: Tunnel, Zone, and the 530 Audit
A perimeter is a claim the edge must prove A hostname resolving…
Security and Business, Bridged: What Trust Actually Costs
The concept of security and business, bridged: what trust actually costs sits…
Email and DNS, Locked Down: The Perimeter Checklist
The one perimeter external systems inspect: DNSSEC signing, SPF/DKIM/DMARC with a reject…
Key Rotation: When Agents Outlive Their Credentials
Key Rotation: When Agents Outlive Their Credentials Draft — S7.5 · series:…
DNSSEC + SPF/DMARC: The Email Perimeter We Actually Hardened
Most security conversations start with the application layer. Firewalls, WAFs, input validation,…
Docker Swarm Persistence: Containers That Survive Restarts
A container that forgets everything when it restarts is not infrastructure. It…
The Narrow Gate, Deep Dive: What the Gate Blocks That Sandboxes Don’t
The Narrow Gate, Deep Dive: What the Gate Blocks That Sandboxes Don't…

Solid-Keys for Humans: Customer-Tier Access as Platonic Solids
When a customer signs up for an AI service, they get a…